19
cross-posted to: https://sh.itjust.works/post/14114626
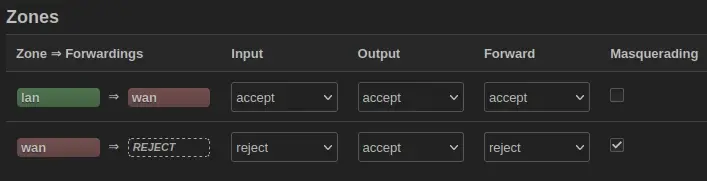
If the rule is about forwarding traffic from the lan interface to the wan interface, then why is there also a forward rule? How would inputs, and outputs make any sense if the rule is talking about forwarding? What does it mean for wan to forward to REJECT? I interperet that as saying that wan doesn't go anywhere, but that wouldn't make sense given that the router can send, and receive over the internet.
For example I would interperet the first rule as follows:
lan => wan: the conditions for which connections from thelaninterface are forwarded to to thewaninterface.Input: accept: thelaninterface accepts all connections originating from the network (I wouldn't understand the point of setting this to bereject).Output: accept: all connections exiting thewaninterface are accepted (again, I'm not sure what the point of this would be).Forward: accept: forwarding of packets fromlantowanis allowed.- Masquerade: I honestly don't know what the effect of enabling this would be. What would it mean to masquerade the
laninterface?
I tried finding documentation, and I did come across this, and this, but, from what I could understand, they didn't really answer any of my questions.
I linked that at the end of my post. I mentioned that I felt it didn't answer my question.
Sorry, I just read skimmed through your post without checking through the links
It's no problem! Thank you for trying to help 😊