[-] cambionn@feddit.nl 28 points 2 months ago

I never understood why not. Dressing up "nicely" doesn't need to be uncomfortable at all. If the clothes fit well and are suitable for the occasion and location you can be comfortable and be dressed nicely.

What I never understood is people going out in pjama's or sportwear while acting like those are the only comfy clothes in the world and the rest of the people are making themselves have a worse time. Be it at airports/planes or elsewhere. Putting on decent pants take 2 seconds and can be just as comfy, so time and comfort aren't really much of an excuse. People should invest in good basics for day to day use, you'll earn it back in daily comfort.

But also, some people simply enjoy looking a certain way. Even for less comfortable clothes, that enjoyment can be bigger than the discomfort making it worth it to them. It's not always about having a reason.

1
submitted 2 months ago* (last edited 2 months ago) by cambionn@feddit.nl to c/vocaloid@ani.social

Only few more to go! Only playing hard mode and higher + no macros.

Anyone else here playing?

14

More context/info below ⬇️

So do you use UPF clothes? What are your favorites? How you combine them to still look nice and fashionable?

Currently, I have a few hoodies from Uniqlo, some boleros and scarfs from Ker Sun, and both full-arm length & short gloves from Sunday Afternoons and Coolibar. I otherwise just wear jeans, t-shirts + undershirts and a baseball cap in summer.


More context/info:

We all know how bad sun damage is for your skin right? It's the number one ager for your skin and biggest cause of skin cancer. I also have PLE (sun allergy) so it's extra important for me. Allergic reactions ain't cute, and having to use heavy medical creams to deal with that isn't great for my skin either due to it's side effects. So prevention is best.

I already wear sunscreen (with good UVA & UVB protection) religiously, but at times it doesn't work ideal (when you're too busy to always reaply in time, sweating a lot, rubbing it off on furniture, etc.) and sometimes you just wanna be lazy and not spend 15 minutes applying it to your whole body to walk to the store nearby.

Hence UV protective clothes (or UPF clothes, as UPF is the rating of UV-blockage). You know, those kinda clothes you see Asians covering themselves with. Protection can be archieved by fabric, weave, colour, and additives like zinq-oxide. Additives however will wash out over time, whereas clothes not relying on them will work until the fabric degrades.

Some pro's are that UPF clothes keep working without needing to be reapplicated for any bodypart that's covered, and they protect from both UVA and UVB, wheras SPF ratings only measure UVB blocking. Using them also saves money over using sunscreen as covered bodyparts don't need sunscreen making me run out less quick.

Yes, regular clothes cover too but their protection is a guess game. A white cotton shirt would have a UPF rating of 3~7 for example. Traditional blue jeans are quite high (100+), but the same jeans in white or thinner fabrics are much lower (not even meeting European standards to be called UV-protective). UPF clothes are tested and certified. In the EU, they need a rating of UPF40 or higher to be allowed to be marketed as "UV-protective".

UV-protective clothes are also often made to still be comfortable in hot weather, wheras other clothes that protect as much might be thicker and warmer. At times it may even be more comfortable than bare skin due to blocking direct sun hitting you and using cooling fabrics.

Sadly most are simple plain (sport)shirts or longsleeves, which is boring after a while, or swimwear. Hence this topic.

Some brands who make UPF clothes:

  • Uniqlo
  • Ker Sun
  • Coolibar
  • Solbari
  • Sunday Afternoons
  • Columbia
  • Hyphen
  • UV.LINE
  • Skinshield
  • iq-uv
  • REI
  • UVSkinz
  • Patagonia
[-] cambionn@feddit.nl 18 points 2 years ago

Average Joe wants an easy all-in-one solution. That's what Google, Apple and Microsoft offer. An ecosystem. If you want to fight that, you need to be able to offer that. So that's what Proton is doing.

Of course it's better to have it seperated. And the security and privacy nerds will likely keep doing that anyways. But Average Joe doesn't want to take a hassle and rather looses privacy than do that.

Issue is, things are only as secure as the least secure point. Average Joe using Google and Microsoft means your data also goes there when interacting. When Average Joe is swayed by a place that is privacy-friendly ánd convinient, it makes your weakest link also stronger.

Meanwhile, Average Joe is also more save then when he was using Google or Microsoft services. Even when he would be less save than if he had his stuff seperated.

It helps everyone.

With that in mind, I applaud it. But I won't use it. I use Proton for mail, Joplin for notes (encrypting them in Joplin and syncing with NextCloud), and my passwords are also elsewhere than ProtonPass.

[-] cambionn@feddit.nl 19 points 3 years ago

No and no. It's not too late, and just watching sitcons won't teach you enough to start speaking. But if you just start actual studying and practicing you can learn it just fine. Watching TV can be used to practice listening, but on it's own it's not enough unless you're a wonderkid.

[-] cambionn@feddit.nl 33 points 3 years ago

I think ActivityPup isn't even integrated into Threads yet? On release they said soon, a week later they said it was long-time planning. Haven't heard about it since.

[-] cambionn@feddit.nl 26 points 3 years ago* (last edited 3 years ago)

Article says:

We’re also beginning the beta for our upcoming macOS desktop app for Proton Drive. [...] Once the macOS app is released, we’ll also work on our planned Linux version.

Based on Proton's trackrecord in development times I'ld say a far future, but I must admit they've been making meters lately when it comes to releasing stuff. It may be sooner than expected (or it might take years, we'd have to wait and see).

[-] cambionn@feddit.nl 119 points 3 years ago* (last edited 3 years ago)

Well outside of the general open source and E2EE stuff, there are a few more things.

They're under a non-profit foundation and charity to which donating is tax-deducatble. That means they have to publicice their financial numbers. Selling data would generate a sudden revenue, which would draw attention.

They also regularily do external audits, both from external audit organisations as individuals. This list was made in august 2022, you can likely find a newer list somewhere. I just did a quick search for you. https://community.signalusers.org/t/overview-of-third-party-security-audits/13243

Signal also runs perfectly fine without anything Google btw. It uses PlayServices only if you have it on your phone (otherwise it just uses WebSockets), as it preserves battery life. However, it doesn't actually send data to Google over PlayServices. Instead it sends an empty notification, which wakes the phone and is recognised by Signal as a trigger to make it connect to Signal servers to grab data directly from there. If you wish, you can check this in the code yourself. I guess you may also be able to confirm this looking at network traffic from and to your phone.

Also a note on the E2EE. Another important thing is that not only the message is encrypted, but also the metadata. Unlike most other chatapps like WhatsApp; who knows where you are, who you talk to, how often, etc. You could theoretically also check this by checking outgoing traffic if you wish.

This also means that unless they somehow secretly have a copy of your private key, there is no data for them to sell anyways. The fact that even in court they've didn't have data to show, them passing many external audits without this being a point (sometimes issues are found, which is normal. If audits are always perfect I'd be more warry. But never on this point afaik), and that nothing in the code nor internet traffic points to them possibly having this, makes me not that worried about the idea that they secretly got a copy of peoples private keys.

So overal while it's perhaps technically possible they secretly run something else on their server and build a back door to read your messages, they are many things that show they don't, and literally nothing that would say they do. And neither does there seem to be any reason why, since they can't sell it nor give it in court. So unless you believe they have some evil bigger plan, I don't see the reason to doubt.

And a little note. Privacy people can be crazy, and I say that in a positive way! If you can check it, people no doubt have, and issues would've been found. Yet many people deep into it still vouch for it. That says something. And the less crazy people profit of this. This is similar to why many big FOSS projects are considered safe even if you didn't check all code yourself. And before you say "but if everyone thinks like that", realise that the craziest don't trust other people either. While smaller projects could hide perhaps, the real big/famous projects like Signal, Linux, LibreOffice, etc would fall trough as soon as they start doing shit.

[-] cambionn@feddit.nl 31 points 3 years ago

I actually used to have YT Premium because I'm a strong believer that nothing is free, so you either pay with data or money (on anything slightly commercial, not counting FOSS projects made as hobby or under foundations etc. as things get more complex then. But even then I pay/donate for some stuff in the same way of reasoning).

Yet I cancled the YT Premium subscription. Simply for one reason, privacy. I don't mind paying, but then I don't want just no adds, I also want no tracking. I pay with money, so I don't want to pay with data as well having a whole profile made.

Switched to NewPipe with sponsorblock on phone and TV and FreeTube on PC. Got a redirect extension in FireFox automatically sending YT videos to either Invidious or Pipe.

1
submitted 3 years ago* (last edited 3 years ago) by cambionn@feddit.nl to c/feddit_nl@feddit.nl

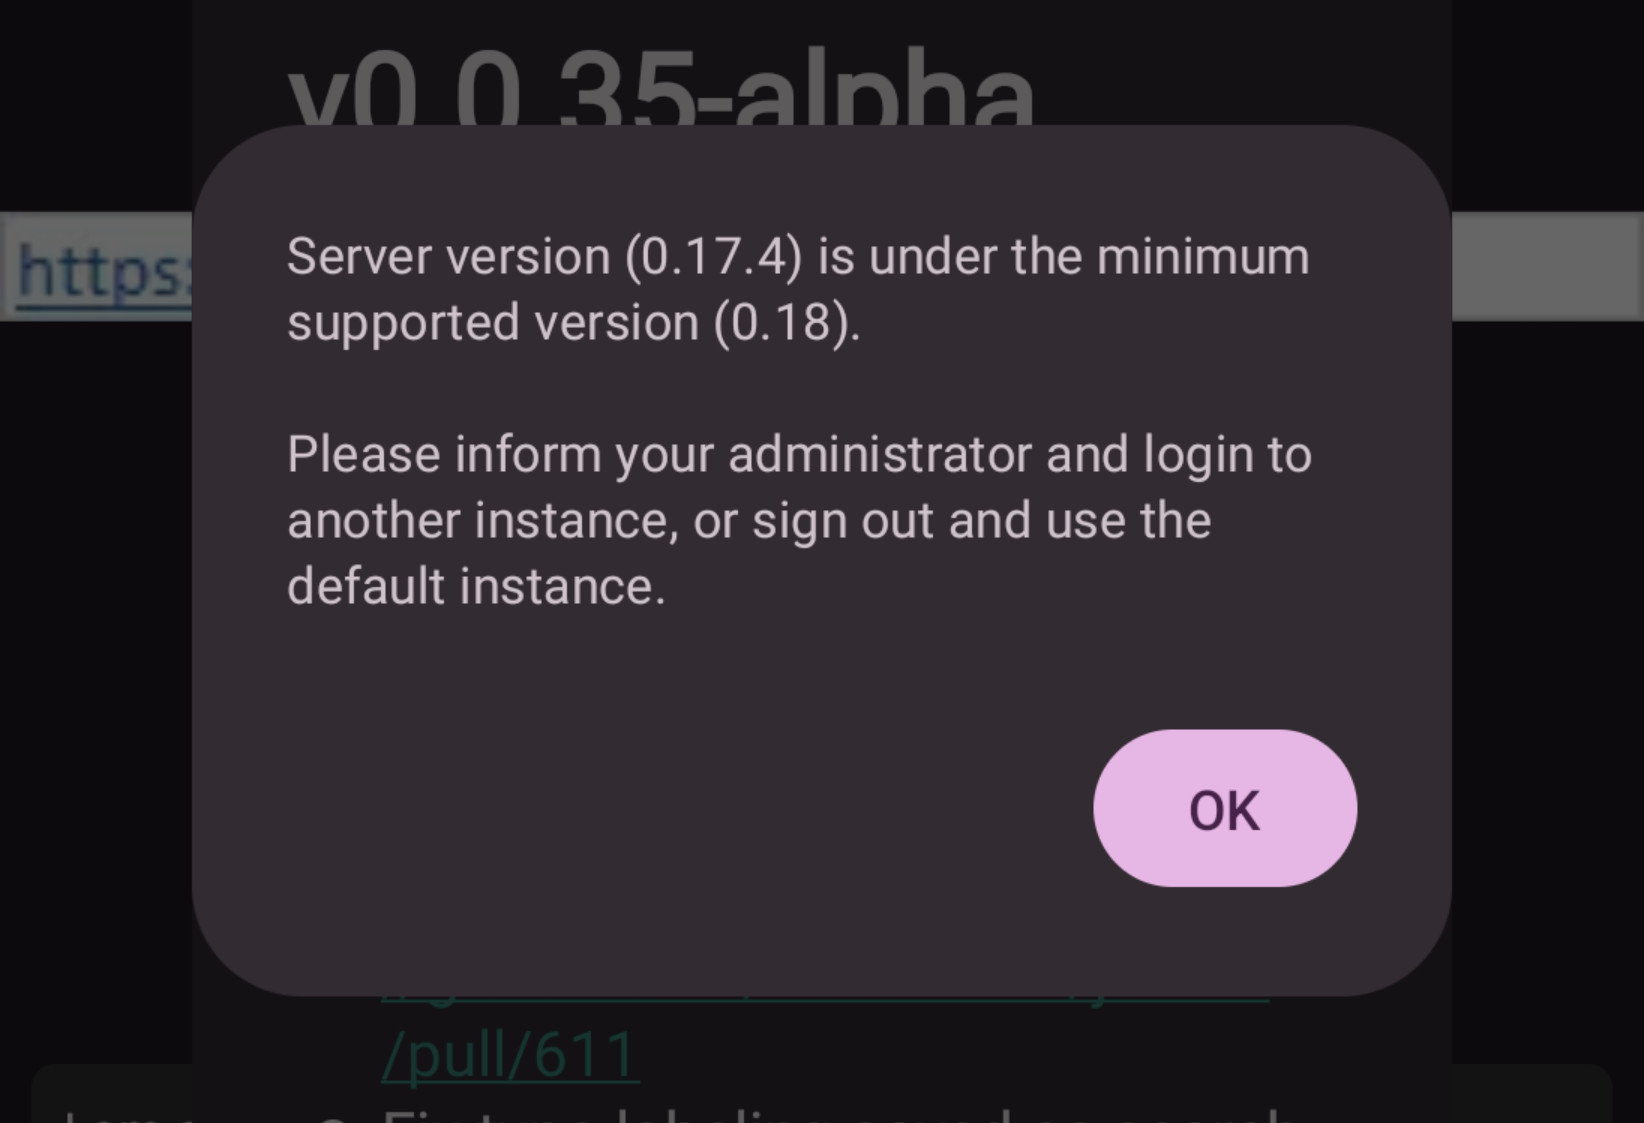
Sinds Jerboa's update gister krijg ik de volgende melding. Alles lijkt nog te werken. Maar gezien de officiele app dit aangeeft, wellicht dat server admin een kijkje wil nemen naar het updaten van de server 🙃

7
Horses (lemmy.ml)

!equestrian@lemmy.ml

Community to discuss riding, horse ownership, and other horse-related things.

4
submitted 3 years ago* (last edited 3 years ago) by cambionn@feddit.nl to c/newcommunities@lemmy.world

find it on !vpop@lemmy.ml

Community to share and discuss Vietnamese pop music

[-] cambionn@feddit.nl 21 points 3 years ago* (last edited 3 years ago)

They said it will be able to connect with Mastodon, so there is zero need imho. I guess it's more aimed at the casual user who doesn't care much about data collection.

What I wonder more tho, how is Meta planning on not getting blocked by most Mastodon servers out of fear they'll go grab all data possible from any server they federate with? Most Mastodon users aren't exactly pro-Meta and pro-give all your data away...

[-] cambionn@feddit.nl 15 points 3 years ago

Well some Discord channels are already synchronising their content with Matrix, using the room feature to mimic the channel structure. OpenStreetMaps does this for example. I wouldn't mind that normalising as at least, it stops me from needing to use Discord myself. But the fact it still synchronises back to Discord is, of course, not ideal. Small steps to the right direction I guess.

Replacement would be nice, but I mainly use it for some local communities which I expect will be the last to migrate. They barely got a start on Discord...

[-] cambionn@feddit.nl 24 points 3 years ago* (last edited 3 years ago)

Well, while everything tarketed to Europeans (having EU domains is enough) should follow GDPR including the right to be forgotten, the whole issue is a bit more complex than most people seem to think.

For one, things not marketed to EU citizen don't count. And the owner of a website, this case the hoster of an instance, is responsible for this. Not the software they use (Lemmy). I don't think Lemmy tracks you specifically, as the code is open source and people likely would've noticed that by now. But servers could theoretically. That's why you need to choose a server you trust, or host your own.

An instance aimed at USA people hosted in the USA doesn't need to be GDPR compliant while a German one hosten in Germany would. An instance aimed at the world hosted in the USA also would, but likely breaks GDPR simply by being hosted in the USA. That's part of why big social media need EU servers.

A federated system is not in one place, and another issue is that while deletion requests could be send (and Lemmy supports this accourding to their website), it can't be as easily enforced to be followed by third parties. Of which, there are a lot in a decentral place.

Think of this: If I post something on Reddit, it get's reposted to 4chan, then I remove my original post, then it's still on 4chan. I could ask them to remove it, but that would likely be declined. Since 4chan has little to do with the EU and it's citizen, and doesn't actively market itself, they have little to do with the GDPR. At best you could make a copyright based claim, but that'll change it into a whole other topic.

Federated systems similarily take eachothers content. It's important to note that generally Federated networks don't push their content to other instances. Instead, other instances grab them from each other. How often has federation not gone smoothly causing deleted Mastodon posts to still show up on otger instances because they grabbed the post but not the deletion request (I've seen it happen multiple times already).

The right to be forgotten forces them to make it anonymous and untracable upon request, but not to delete every word you ever typed. Anonymising your account and deleting traceble info only would be enough. That means, if the server you requested to deletes their part + send a request to third parties they deliberatly send info to themselves, they did their job as far as law is concerned.

Any third party that grabbed the info by themselves, would require you to send a new request to them. Considering federation works by grabbing other instances, not by pushing your instance to others, any federated post that still has your old info could still be up if changes or deletion requests haven't been processed.

So is Lemmy bad for privacy by default? Not anymore than the rest of the web, as long as you understand that the whole point of decentral systems mean it's not one place. Best to always keep in mind that everything on the internet is forever and public, even if you delete it or use filters on who can see it, as you can never ensure no one copies it and post it elsewhere.

[-] cambionn@feddit.nl 14 points 3 years ago

If your issue with Mastodon was mainly the interface, maybe you could try using a third party app like Tusky. Mastodon's own app isn't great, but when using Tusky it's quite nice.

I was never a fan of Twitter, but I use Mastodon quite a bit. Both for following news and projects as for just posting random crap. I never used Reddit much either, only read when it would come up on an online search. But Lemmy so far has been nice, if not a bit silent. I've got good hope for it.

[-] cambionn@feddit.nl 15 points 3 years ago

Don't get me wrong, I'd love for them to die and for federated or privacy-conscious alternatives to take their place. But I don't think they're all dying that much.

While it is true that more people complain and leave for alternatives than before, long term it doesn't seem like the masses are really switching yet. I feel like people are becoming more aware of privacy, market-monopoly, and other related issues, but at the same time don't want to hand in convinience, pay money to stop it, nor move somewhere when the rest isn't there yet. We see a spike on alternative SNS like Lemmy and Mastodon around the time news regarding some drama with big SNS releases, but we also see many users leave the alternatives after a time and that they never left the first platform that had drama to start with. They're just used both to eventually return. It's generally only a specific crowd that really leaves for good to go elsewhere, but not the masses.

As for the many lay-offs lately. Don't forget that during COVID the sky was the limit for tech. They all predicted that after the time being locked in our houses doing everything remotely, we'd keep doing that, and they invested accourdingly. However, as the world opened up more that predictioned turned out wrong, causing them to have over-invested and needing to make budget cuts to fix their mistake.

view more: next ›

cambionn

0 post score
0 comment score
joined 3 years ago