19
FF140: Disable DRM icon in browser bar?
(infosec.pub)
I've tested kagi and agree that the search results are great. What I don't like is that it's making anonymous searching impossible, since I have to be logged in to use it (or use my unique token as part of the url for mobile searches).
Ultimately this means to me that in a private window mode (or even logged out with a fingerprinting resistant browser) I do not have the same degree of anonymity I enjoy even when using Google, let alone DDG or others.
I like the idea of not being dependent on google, but exposing my entire search history to one single entity is not my answer of choice.
Firefox my beloved.
Escalate it to the EU consumer watchdog, they got some real teeth.
https://commission.europa.eu/live-work-travel-eu/consumer-rights-and-complaints_en
Assuming you bought the Italian version because you're living in Italy.
Best case, you get your money back.
To avoid such issues in the future, CrowdStrike should prioritize rigorous testing across all supported configurations.
Bold of them to assume there's a future after a gazillion off incoming lawsuits.
cross-posted from: https://infosec.pub/post/14206569
Hi all,
First off: Can't switch to Linux, Windows is a work requirement. Please spare me.
With that out of the way, here's my problem:
Since 2-3 days I've been seeing ads disguised as a minimized video player popup on my Windows 10 Login Screen
.
Initially I thought I might have been watching something on youtube and forgot to close the tab and it autoplayed in the background until reaching this stuff by chance; but that turned out not to be the case (I'm also using Firefox exclusively, which I thought wouldn't integrate with Windows, but I wasn't 100% sure on that end).
I tried to research this a bit, but the only similar case I found was in an old reddit thread saying that some Windows update installed the LinkedIn App for them, which is not the case here.
Antivirus (Bit Defender) and Malwarebytes both give me a clean report.
So I did some more digging and right click that thing with my firewall set to deny all to figure out where this is taking me, and surprise...
There's a total of 100 connection attempts from Windows Search to around 10 different IP addresses, all of which belong to Microsoft.
I have not installed any updates in the last 14 days, no new software, and have not changed any system settings.
What did change is that I am currently not in China, where I normally live, but am on a business trip to Malaysia, where a bunch of services that are blocked in China might be accessible, and are now splicing in those (somewhat disguised) ads.
Does this happen to anyone else, and if so, do you have an idea how to get rid of it?
Thanks a lot in advance!
Hi all,
First off: Can't switch to Linux, Windows is a work requirement. Please spare me.
With that out of the way, here's my problem:
Since 2-3 days I've been seeing ads disguised as a minimized video player popup on my Windows 10 Login Screen
.
Initially I thought I might have been watching something on youtube and forgot to close the tab and it autoplayed in the background until reaching this stuff by chance; but that turned out not to be the case (I'm also using Firefox exclusively, which I thought wouldn't integrate with Windows, but I wasn't 100% sure on that end).
I tried to research this a bit, but the only similar case I found was in an old reddit thread saying that some Windows update installed the LinkedIn App for them, which is not the case here.
Antivirus (Bit Defender) and Malwarebytes both give me a clean report.
So I did some more digging and right click that thing with my firewall set to deny all to figure out where this is taking me, and surprise...
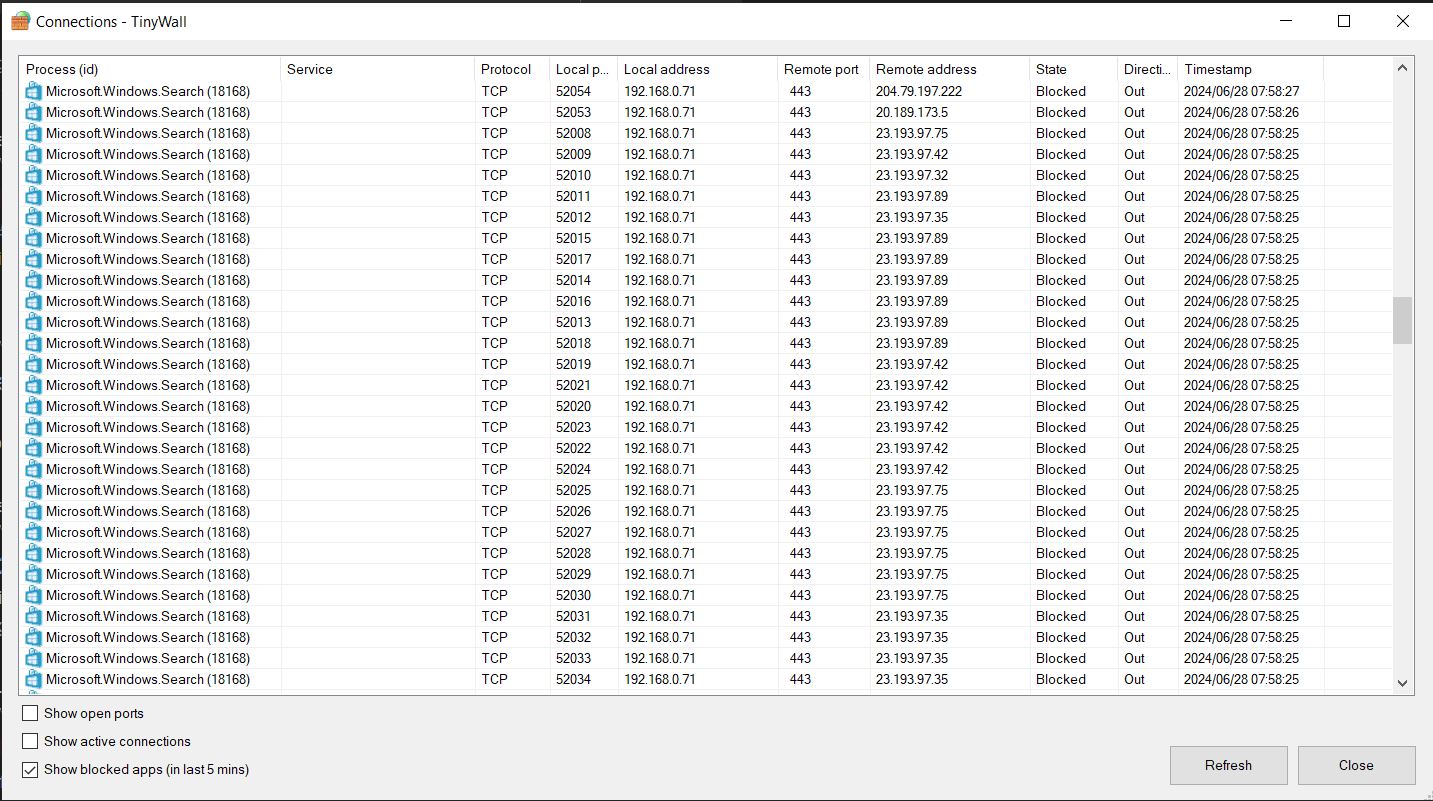
There's a total of 100 connection attempts from Windows Search to around 10 different IP addresses, all of which belong to Microsoft.
I have not installed any updates in the last 14 days, no new software, and have not changed any system settings.
What did change is that I am currently not in China, where I normally live, but am on a business trip to Malaysia, where a bunch of services that are blocked in China might be accessible, and are now splicing in those (somewhat disguised) ads.
Does this happen to anyone else, and if so, do you have an idea how to get rid of it?
Thanks a lot in advance!
Reads like thinly veiled advertising for the services offered by the website this article comes from. I doubt it's anywhere close to a representative sample.
German here, there are a bunch of "buts" worth mentioning, before everyone mistakes our country for a socialist utopia:
For starters, the notice period for employee and employer are identical, mutually agreed upon, and can be 1-6 months. If the OP was fired with 3 months notice, that simply means he would have to give equal notice when resigning. Usually it's however expected to work all through the notice period and not just relax at home.
Secondly, a compensation is voluntarily, unless being fired due to socio-economic circumstances (as opposed to bad performance). In such a case, 1 month compensation per 1 year worked is often recommended by labor courts (maxing out at 6 months). Again, those are not mandatory unless it goes to an arbitration tribunal or court.
Thirdly, being allowed to take classes or other further education measures typically only exists for elderly layoffs with limited chances of finding qualified employment, or people with very limited skillset. Again the only exception is when being terminated due to socio-economic reasons, where the company agrees to pay development measures as part or in lieu of a settlement.
Unemployment benefits apply once the employee has paid social security contributions for minimum 12 months without interruption. In the first year they are due to receive 70% of their former salary after tax (there's a cap though, I believe it was 2800 EUR/month).
If they still didn't secure a new job, they are entitled to receive 484 EUR plus housing (based on actual cost; again capped and with a size restriction, I believe it was max. 20m² per person in the household). To qualify for this second stage of benefits however, the person must not have any assets exceeding 10k EUR, else they'd have to use those up first).
Medical insurance however is available all through without any caveats.
Hi all,
Just updated FF to 124.0.1 and now the whatsapp web view is broken. The text input field is somewhere in the upper third of the screen and in the background, overlayed by text boxes so that I can't actually select it. It's automatically selected when switching from one chat to another so I can type there, but only blind in most cases since any comment boxes overlap it.
Tried restarting, clearing cookies, re-authenticating, disabling all plugins, nothing worked.
Does anyone experience something similar and/or know a workaround?
Thanks!
Edit: Fixed by logging out of whatsapp web, clearing cookies, restarting the browser, and then logging back in. Neither of the steps had worked on its own previously, but the combination did the trick.

CNET lost my trust when they repacked software and drivers in their archive with a homebrew installer that bundled bloatware. Initially the bing search bar, then Opera, latest I remember was some antivirus solution. Sure, you can deselect them all, but I hate those business practices with a passion.
Lawyer time. At will, maybe. But you've been assaulted on the job, are now suffering from severe anxiety (right???), and got fired on top of it? They'll eat your boss for breakfast and get a nice severance package out of it.
Mark Rober.
He got louder, flashier, less techy and more talky and is doing a gazillion reruns of the same general idea over and over. Can't really enjoy it anymore.
I don't really use facebook anymore so couldn't care less; but so happened to log in today to change my password and saw this on my front page.

Time to ban Twitter and call it a day.
We learned swimming in primary school in Germany, no opting out.
But having lived in several African countries and now in China, it's surprising how many people not only can't swim, but are deathly afraid of water.
This fucking clown is going to push the whole world into a new recession.