587
submitted 2 years ago* (last edited 2 years ago) by sorter_plainview@lemmy.today to c/programmer_humor@programming.dev

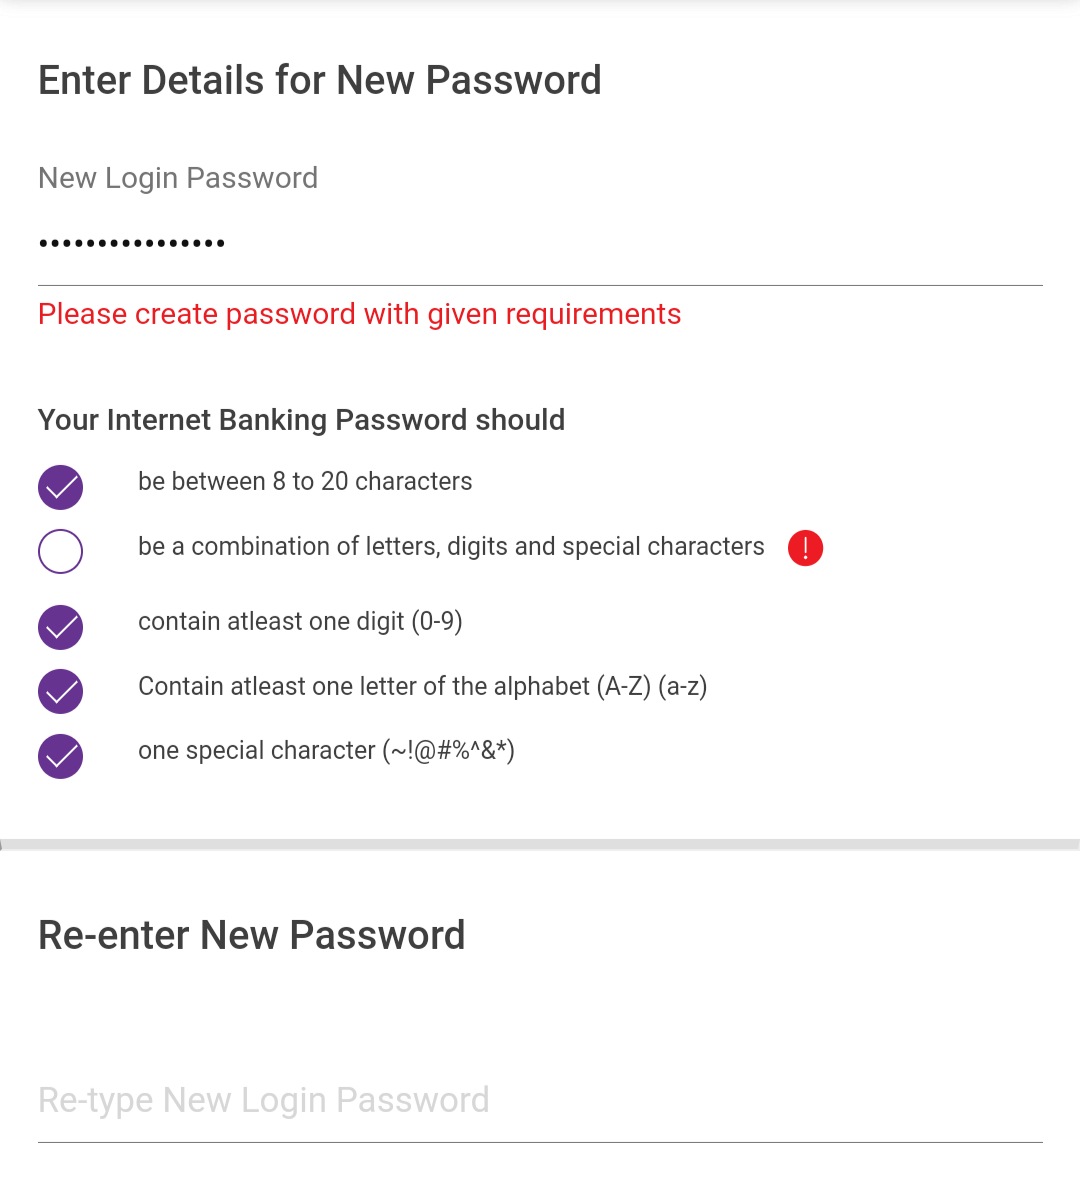
Edit: @Successful_Try543@feddit.org solved it. It says "one special character". Not "at least one".
top 50 comments
sorted by: hot top new old
[-] xmunk@sh.itjust.works 221 points 2 years ago

It's fucking insane that an internet banking portal has such a low cap on max characters and such shitty rule enforcement.

[-] sorter_plainview@lemmy.today 90 points 2 years ago

Their desktop site is even more shitty. It won't allow right click or paste actions. There goes compatibility with password managers.

[-] superkret@feddit.org 57 points 2 years ago

Bitwarden has a function where it types in (not pastes) the password and shows the prompt for it without right-click.

[-] Appoxo@lemmy.dbzer0.com 17 points 2 years ago

And even if theres an app for Windows (https://github.com/jlaundry/TypeClipboard) that can type it for you and even has a shortcut.
I am sure someone in the linux world knows an equivalent tool.
We use it at work to paste long passwords when remoting in.

load more comments (2 replies)
[-] xmunk@sh.itjust.works 37 points 2 years ago

As a super secret dev hack may I introduce you to shift + insert a fair few sites specifically block ctrl + v instead of properly disabling the clipboard action and, of course, if you read this and then submit a Jira ticket to block shift + insert... well... h8u

[-] LuycYQ2uUiTjR3yLri@sh.itjust.works 21 points 2 years ago

You can also drag the password in from another text field instead of pasting

[-] independantiste@sh.itjust.works 14 points 2 years ago

I usually to in the developer tools and manually disable the thing preventing the paste action. It's usually a string to remove some JS or something or an Event that you need to uncheck

[-] xmunk@sh.itjust.works 17 points 2 years ago

If you're opening up the dev tools you can also paste your string directly into <input value="" /> unless something weird is going on.

load more comments (1 replies)
[-] Creat@discuss.tchncs.de 17 points 2 years ago

Any password manager should be able to "type in" the password. Or be a browser plugin that doesn't rely on copy pasting, but use other mechanisms to inject it directly into the field.

But yes, if that's their online portal, I am not kidding I would change banks.

[-] stealth_cookies@lemmy.world 32 points 2 years ago

My bank's password used to have to be exactly 6 characters, no special characters and you could use numbers and letters interchangeably because it was also your phone banking password.

[-] hushable@lemmy.world 42 points 2 years ago* (last edited 2 years ago)

a previous bank used to have a max password length of 8 characters, then proudly announced that they will increase it to 32

Then I made a typo at the end of my password and it let me in anyway, and I realised they were just trimming the first 8 characters to give the illusion of security

[-] Wizard_Pope@lemmy.world 15 points 2 years ago

That is so insane. To think they would rather just clip the passwords instead of habing it be longer.

Did you try out your hypothesis by using the first 8 letters than just random junk until you hit your password length?

[-] hushable@lemmy.world 16 points 2 years ago

I tried then first N characters of my password until I found out the threshold was at 8, then I tried with the first 8 chartacters of my password and then random junk and it worked.

I also had two friends in the same bank to validate

[-] Wizard_Pope@lemmy.world 12 points 2 years ago

Unbelievable.

load more comments (1 replies)
[-] DudeDudenson@lemmings.world 26 points 2 years ago

Visa has a hard limit of 8 and requires the first 4 to be numbers because the phone tree might require it as a password

The whole banking industry is ridiculous and is ridiculously legislated

load more comments (1 replies)
[-] Flipper@feddit.org 19 points 2 years ago

The ERP software I have to use has a strict limit of 6 characters as password. Only alphabet and numbers allowed.

Maybe when I leave I try an SQL injection.

[-] ICastFist@programming.dev 9 points 2 years ago

Bobby tables, noooooooo!

[-] ImplyingImplications@lemmy.ca 12 points 2 years ago

I had to create an account on a government website. The website didn't list a character limit so I used a password manager to generate a 32 character password. My account was created but I couldn't log in. I used the "forgot my password" option and I received an email of my password in plain text. I also noticed why I couldn't log in. The password was truncated to just 20 characters. Brilliant website! Tax dollars at work!

[-] kirk781@discuss.tchncs.de 8 points 2 years ago

Some internet banking sites give access after only asking for login password. They will only ask for transaction password and OTP (that will only come on phone) later on. Asking for two passwords isn't necessarily more secure since many people will just reuse their original one again. And OTP instead of offering something like hardware security key is insane.

load more comments (2 replies)
load more comments (17 replies)
[-] Successful_Try543@feddit.org 122 points 2 years ago* (last edited 2 years ago)

It says one special character, not at least one. Maybe the password has more than one.

[-] sorter_plainview@lemmy.today 102 points 2 years ago

Holy shit!! You did it. I would never expect a banking password to max special characters. I have been scratching my head with Bitwarden and this shitty app for an hour.

[-] FederatedSaint@lemmy.world 48 points 2 years ago

But wouldn't that mean the bottom checkbox should be cleared and the 2nd one should be checked?

Still doesn't make sense.

[-] sorter_plainview@lemmy.today 22 points 2 years ago

Yeah that's true. The UI does not accurately represent the validation conditions.

[-] Panda@programming.dev 10 points 2 years ago

Yes, the 2nd one implies that there should be more than one.

load more comments (2 replies)
[-] tooLikeTheNope@lemmy.ml 19 points 2 years ago* (last edited 2 years ago)

Yeah but It still states "A combination of letters, digits and special charaters"

It should then be spelled as "A combination of letters digits, and one special character"

[-] superkret@feddit.org 13 points 2 years ago

It's like a Captcha that only lets in autistic people.

[-] kionite231@lemmy.ca 10 points 2 years ago

You solved the puzzle! here is a cookie for you :D 🍪

load more comments (1 replies)
load more comments (2 replies)
[-] xoggy@programming.dev 64 points 2 years ago
load more comments (8 replies)
[-] superkret@feddit.org 55 points 2 years ago

It says “one special character”. Not “at least one”.

oh. oh god. what the fuck.

load more comments (1 replies)
[-] oo1@lemmings.world 47 points 2 years ago

If >1 special character is not allowed the last check should be failed . The second check is literally satisfied even if there are 2+ specials.

I'd not be using that bank.

[-] refalo@programming.dev 28 points 2 years ago

Now imagine how many services just silently cut off your password at 8 characters and people never notice.

UltraVNC is very guilty of this.

[-] Scoopta@programming.dev 16 points 2 years ago

Wells Fargo cuts to 14 on their sign in page but not on their change password page, ask me how I know

[-] Buddahriffic@lemmy.world 12 points 2 years ago

Once upon a time, battle.net passwords weren't case sensitive. I used upper and lower case letters in my password then one day realized I didn't hit shift for one of the caps as I hit enter out of habit, but then it still let me in instead of asking for the password again.

It was disappointing because it takes more work to remove case-sensitivity than to leave it. I can't think of any good reason to remove it. At least the character limit had a technical reason behind it: having a set size for fields means your database can be more efficient. Better to use the size of a hash and not store the password in plaintext, so it's not a good reason, but at least it's a reason.

load more comments (6 replies)
[-] tofubl@discuss.tchncs.de 21 points 2 years ago
load more comments (1 replies)
[-] Matriks404@lemmy.world 21 points 2 years ago

Your Internet Banking Password should one special character (~!@#%^&*)

Great grammar on their part.

[-] WhiskyTangoFoxtrot@lemmy.world 9 points 2 years ago

Yeah, they noticed their mistake too late, hence the expletive.

load more comments (1 replies)
[-] TheSealStartedIt@lemmy.world 16 points 2 years ago* (last edited 2 years ago)

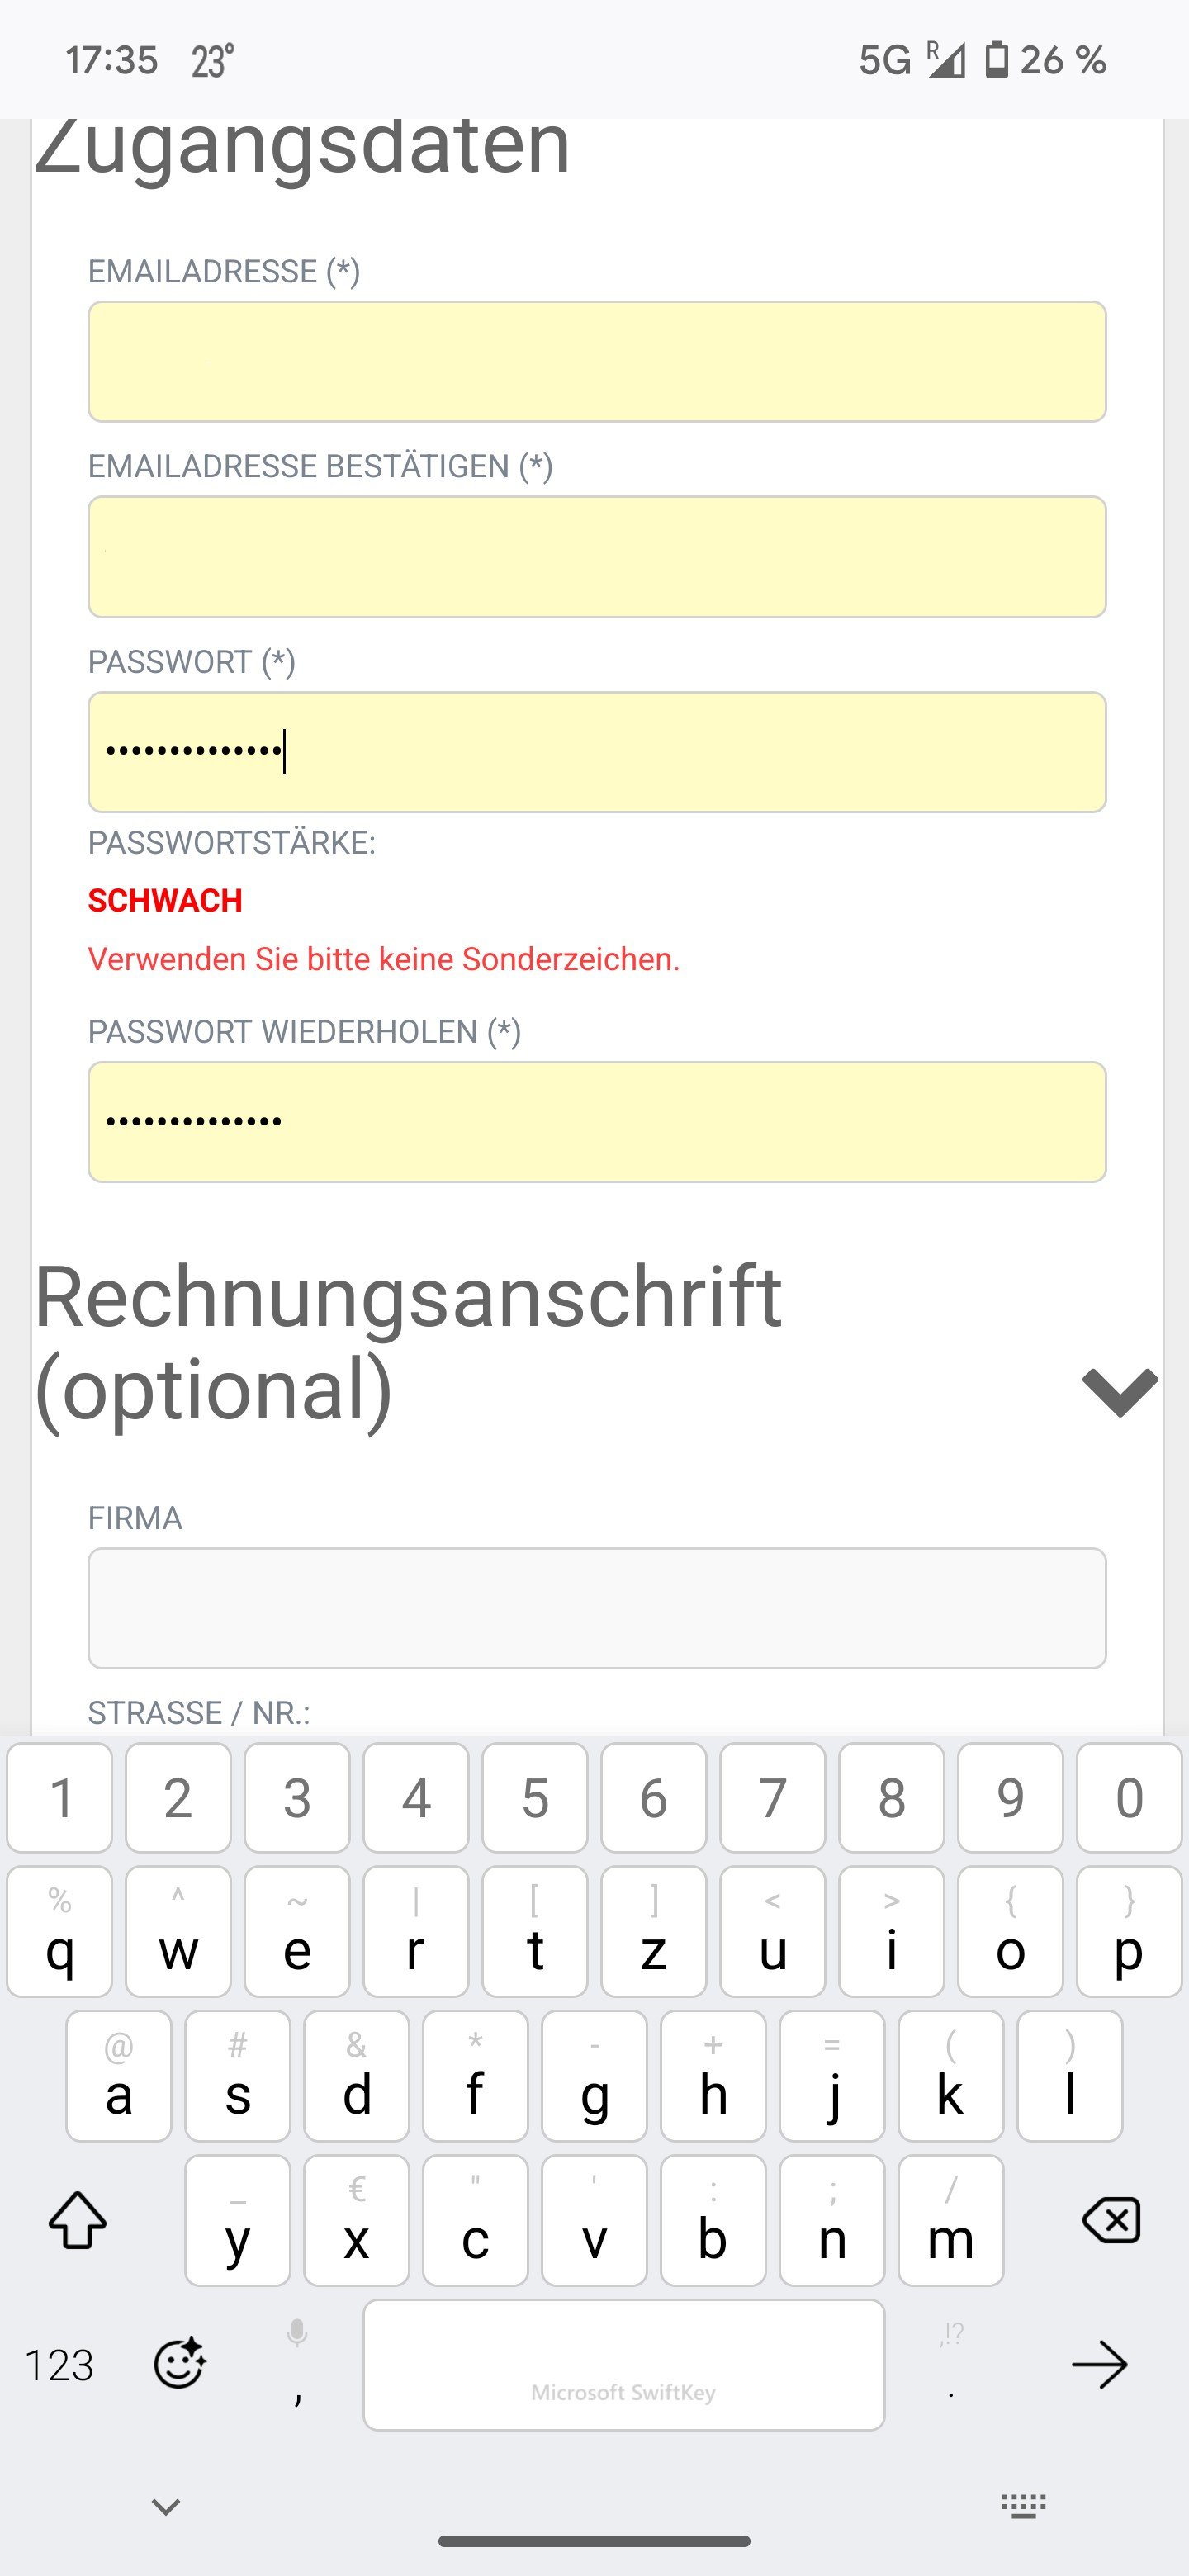
This was a new one for me:

this was a new one for me

Translation: Password strength: weak. Please don't use any special characters.

It was a generated 14 char password.. (╯°□°)╯︵ ┻━┻)

[-] robdor@lemmynsfw.com 16 points 2 years ago

Maybe you accidentally did a permutation instead of a combination.

[-] Artyom@lemm.ee 12 points 2 years ago
load more comments (2 replies)
[-] FuglyDuck@lemmy.world 11 points 2 years ago

My guess is they mean, one capital letter, one lower case letter, a number, and a special character

what's always amused me about these rules is that they exist because people are dumb. Technically, they lower the difficulty of the passwords slightly. ( for example, knowning that one character is a number reduces it to 10 options in stead of 10+26+26+whatever set of special characters)

anyhow. people should use password managers. just saying.

[-] merc@sh.itjust.works 11 points 2 years ago

Noone should of aloud this code to go out the door. Atleast alot of other people people probably complained aswell, so your apart of a bigger group, incase you were worried.

spoilerAnd yes, this was painful to type.

[-] corsicanguppy@lemmy.ca 10 points 2 years ago* (last edited 2 years ago)

Please tell me someone didn't buy software with 'atleast' spelled like that in there. Please, tell me someone tested the web app and had the brains God gave a douglas fir and knew that wasn't a word; that it was never a word; that the writer's spell check should have picked that up; that it's not been over-ruled by stupid so much that it just takes it.

load more comments
view more: next ›
this post was submitted on 09 Sep 2024
587 points (99.5% liked)

Programmer Humor

33218 readers
1206 users here now

Welcome to Programmer Humor!

This is a place where you can post jokes, memes, humor, etc. related to programming!

For sharing awful code theres also Programming Horror.

Rules

founded 3 years ago
MODERATORS